Sample mobile report · 30 pages · PDF
What a mobile test finds once you unzip the app.
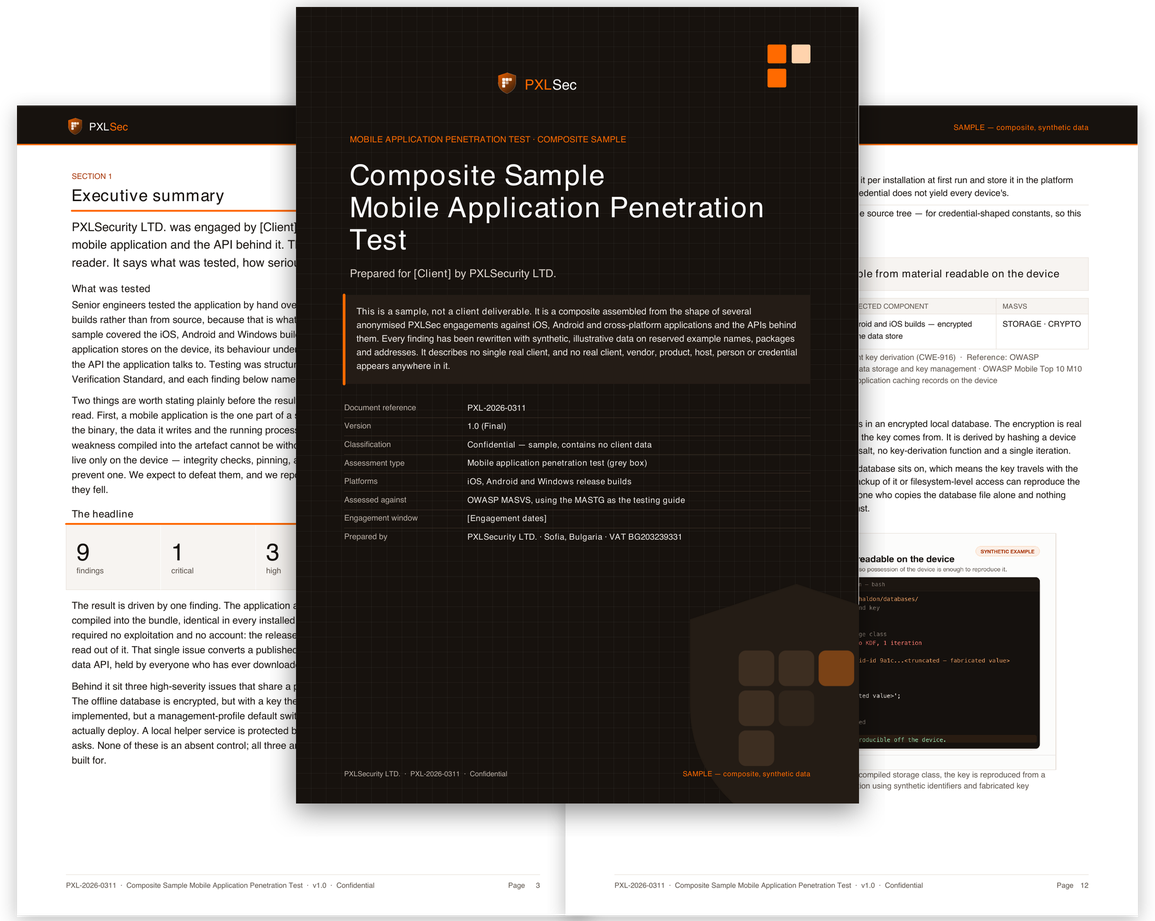
The findings that matter in a mobile engagement are rarely the ones a scanner reports. This is the whole deliverable: nine findings written out in full across the shipped binary, the data at rest, the runtime controls and the API behind the app — each mapped to the OWASP MASVS control group it belongs to.
What’s inside
Nine findings, and the order an attacker finds them in
Executive summary
Why a secret inside a shipped artefact is a different kind of problem from one on a server.
Scope and methodology
The five stages and the eight MASVS control groups, with the findings each produced.
The shipped binary
What reverse-engineering the release build gives away before anyone has an account.
Data on the device
Offline stores, key derivation, logs and backups — and why “encrypted at rest” can mean very little.
Runtime and resilience
Pinning, root and jailbreak detection and anti-tampering, rated on what they protected rather than on being bypassed.
Remediation plan
Three waves, starting with the one action that is not a code change.
Why people ask for it
Because the app is the part you hand to the attacker
Every other target you own sits behind something you control. A mobile app does not: once it is published, the binary, the local data store and the running process belong to whoever installs it. This report is written in that order — artefact first, runtime second, API last — because that is the order the work actually happens in.
It is a composite sample: assembled from the shape of several anonymised engagements, with synthetic illustrative data throughout. It describes no single real client, and no real host, package, person or credential appears in it. No device model, framework version or commercial tool is named as a client’s.
One deliberate choice is worth flagging. The root-detection bypass is rated Medium, not Critical. Defeating a client-side resilience control on a device the attacker owns is expected; what matters is what the control was protecting. A report that leads with a jailbreak bypass is usually padding.
- Scoping a mobile testUse the MASVS coverage table as the basis for your own scope.
- Judging a proposalCompare it against a report that stops at the manifest and the permission list.
- Briefing engineersShow the team what a mobile finding looks like with runtime proof attached.
- Preparing for a customer reviewSee the evidence an enterprise buyer is likely to ask for.
Want this for your own app?
Tell us what you want to protect. A senior tester will help you agree the scope and next steps. We usually reply within one business day.
Confidential from the first conversation
We can sign your NDA before you share sensitive details. Your enquiry is covered by our privacy policy.
How we protect your information · Privacy policy