Sample firmware report · 18 pages · English PDF
From the firmware to the evidence.
Get the complete English sample by email. Five detailed synthetic findings distinguish static analysis, QEMU and device evidence. All scenarios and outcomes are fictional illustrations; no client assessment was executed.
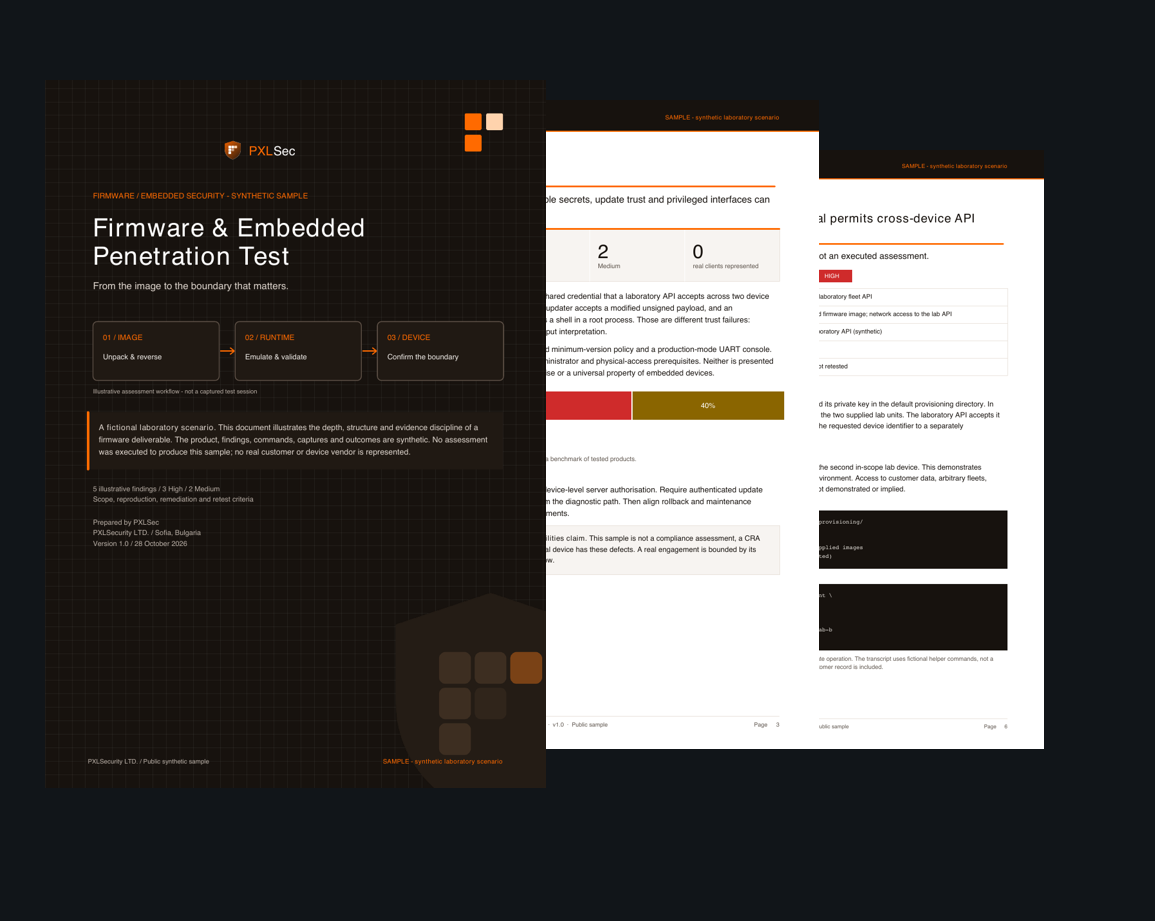
What’s inside
A complete deliverable, clearly labelled
Executive summary and scope
Attacker assumptions, targets, environments and limitations.
Five complete findings
Shared secrets, updates, command injection, rollback and UART.
Evidence provenance
Static analysis, emulation and device checks labelled separately.
Reproduction and impact
Steps, negative controls and boundaries on the conclusions.
Practical remediation
Changes to identity, updates, execution and maintenance.
Retest plan
Measurable closure criteria; no fictional fix is marked as retested.
Why people ask for it
Evaluate the work before you scope it.
This is an entirely synthetic laboratory sample, not a real client report, device-vendor assessment or executed test. Commands and output are illustrative, not captured evidence.
An image review, an emulated result and a hardware check support different conclusions. The sample shows how those differences are documented.
- Compare providersInspect the evidence discipline and specificity of fixes.
- Prepare your scopeDecide whether image, device, source or cloud access is needed.
- Brief engineeringShow a reproducible finding and its retest acceptance criteria.
Want this for your own product?
Tell us what you want to protect. A senior tester will help you agree the scope and next steps. We usually reply within one business day.
Confidential from the first conversation
We can sign your NDA before you share sensitive details. Your enquiry is covered by our privacy policy.
How we protect your information · Privacy policy