Sample Internal / AD report · 24 pages · PDF
Follow the assessment. See how access grew.
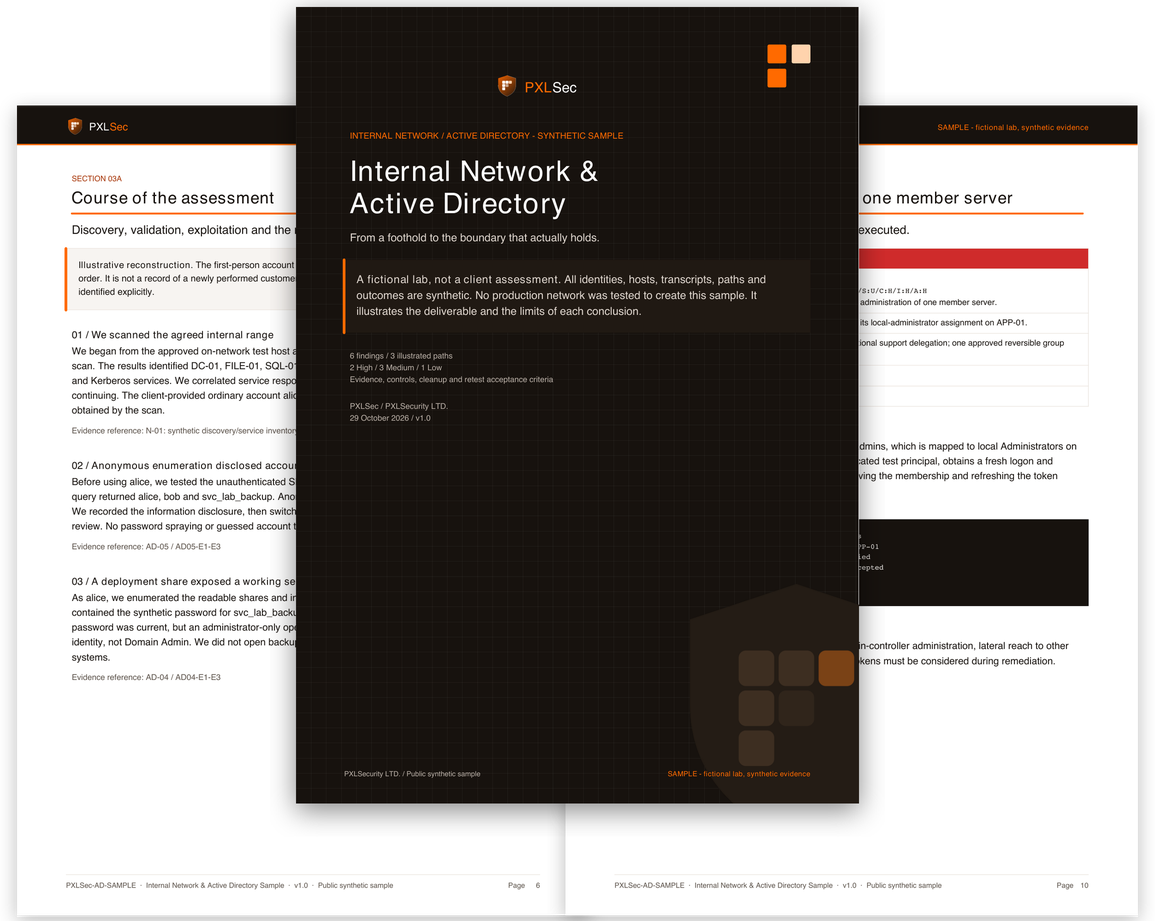
Read how the assessment unfolded: discovery, exposed credentials, privilege escalation, a lab domain hash and server access, followed by six detailed findings and their fixes. This is a fictional lab reconstruction, not a real client assessment.
What’s inside
How the test unfolded
Executive summary and scope
Starting identities, targets, exclusions and the decisions to make first.
Course of the assessment
From service discovery and exposed credentials to privileged authentication, a lab domain hash and server access.
Six findings in full
Cause, evidence, reproduction, impact and a specific repair.
Negative controls
Denied operations and unproven continuations are shown alongside successes.
Cleanup and ownership
Reversed membership changes, session handling and a real-delivery evidence checklist.
Retest and closure
Path-specific acceptance criteria. No fictional finding is marked as retested.
Why people ask for it
From the first scan to the final finding.
Follow the tester decisions: why an observation prompted the next check, how exploitation was validated, and which new access it actually provided. The detailed findings retain the reproduction evidence and engineering fixes.
All hosts, accounts, commands and outcomes in this document are synthetic. The sample does not claim an executed client engagement, a certification or a guarantee of a secure domain.
- Compare providersInspect how conclusions are tied to evidence.
- Scope an internal testChoose on-network and assumed-breach starting positions explicitly.
- Brief your engineersReview the remediation and retest criteria before the engagement.
Want this for your own environment?
Tell us what you want to protect. A senior tester will help you agree the scope and next steps. We usually reply within one business day.
Confidential from the first conversation
We can sign your NDA before you share sensitive details. Your enquiry is covered by our privacy policy.
How we protect your information · Privacy policy